Hosted checks, workflows and secrets
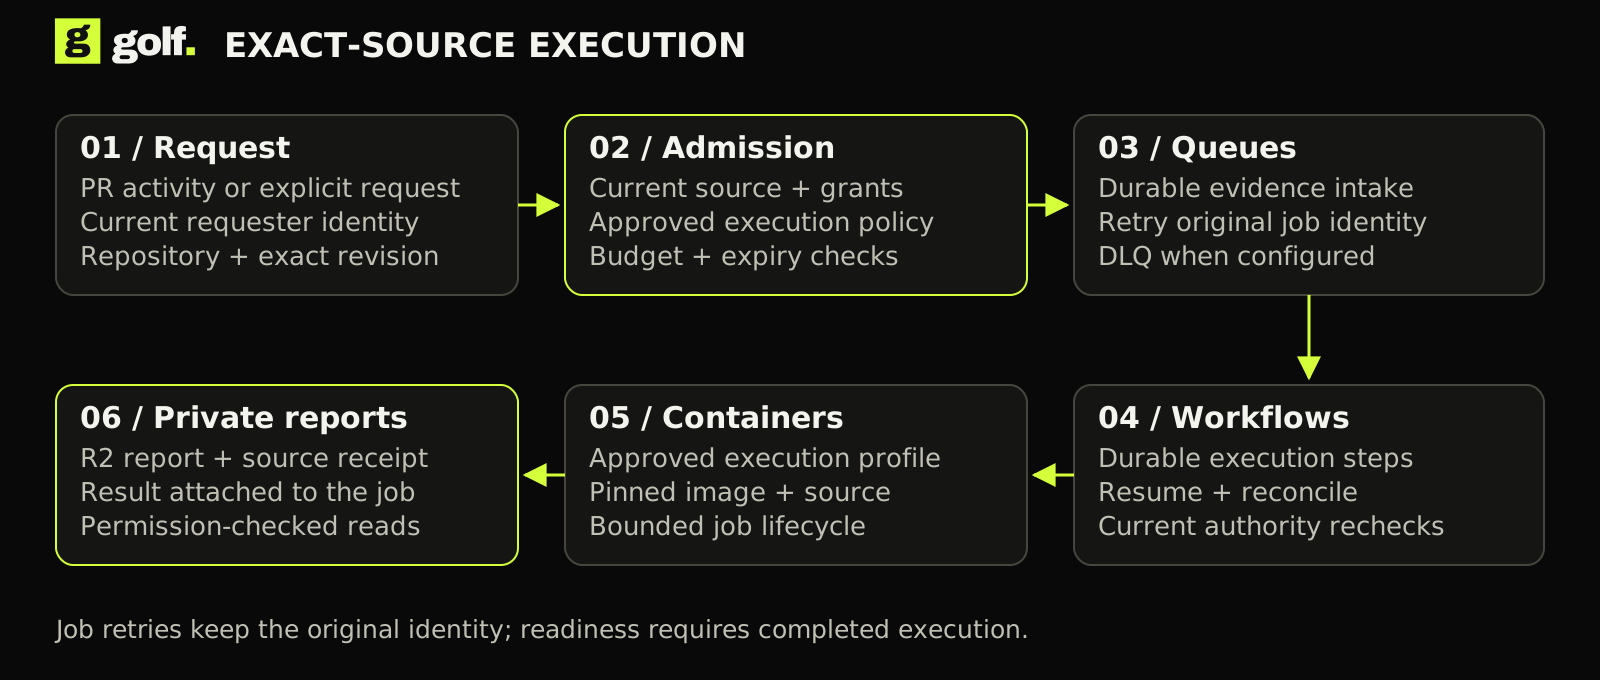
Editable Mermaid source · All architecture diagrams.
Evidence pipeline
Queues buffer admission; Workflows retain stages; Containers execute approved images. None replaces Golf repository authority. Source change, sponsor revocation, expiry and stale work are checked at defined boundaries. Failed or cancelled work is not passing evidence.
Supported workflow profiles
Native hosted PR checks support an approved Python module and one operator-approved Actions shell workflow. Workflow settings inspect up to 20 default-branch files of 64 KiB and start nothing. The Actions page shows the latest 50 stored PR runs.
A repository administrator can disable PR runs and configured automatic push tests at admission. This does not cancel admitted jobs or govern proposals. Native manual dispatch, general branch/tag events, workflow editing, all Actions semantics and full GitLab compatibility remain open.
Repository values
Native secrets and variables are AES-GCM ciphertext in D1 under a dedicated Secrets Store key. Current Access-verified repository administrators manage them with receipts and version fences. Inventory never returns secret values.
Only an administrator-approved exact commit/head branch of the installation-approved PR workflow receives values; approvals last at most 24 hours. Agent jobs, customer runners, manual dispatch, organization/environment values and secrets expressions do not receive them in this slice.
The retained hosted proof showed a secret reaching a workflow step and masked in stored output. Masking detects exact secret text only; transformed values are not covered. Keep secrets out of source and arbitrary output. Rotation and approved external egress remain separate work.
Image distribution
New installations use Cloudflare's managed registry. Golf retains repository/job admission and digest receipts while provider credentials remain broker-only. Broader image scanning, trust and retention policy remain separate acceptance.