Architecture visual guide
Ten original SVG diagrams explain the system by responsibility and workflow. Open an image for full-size detail; each has an editable Mermaid source. These diagrams distinguish current, optional and in-development behavior, and do not grant access or prove new product acceptance.
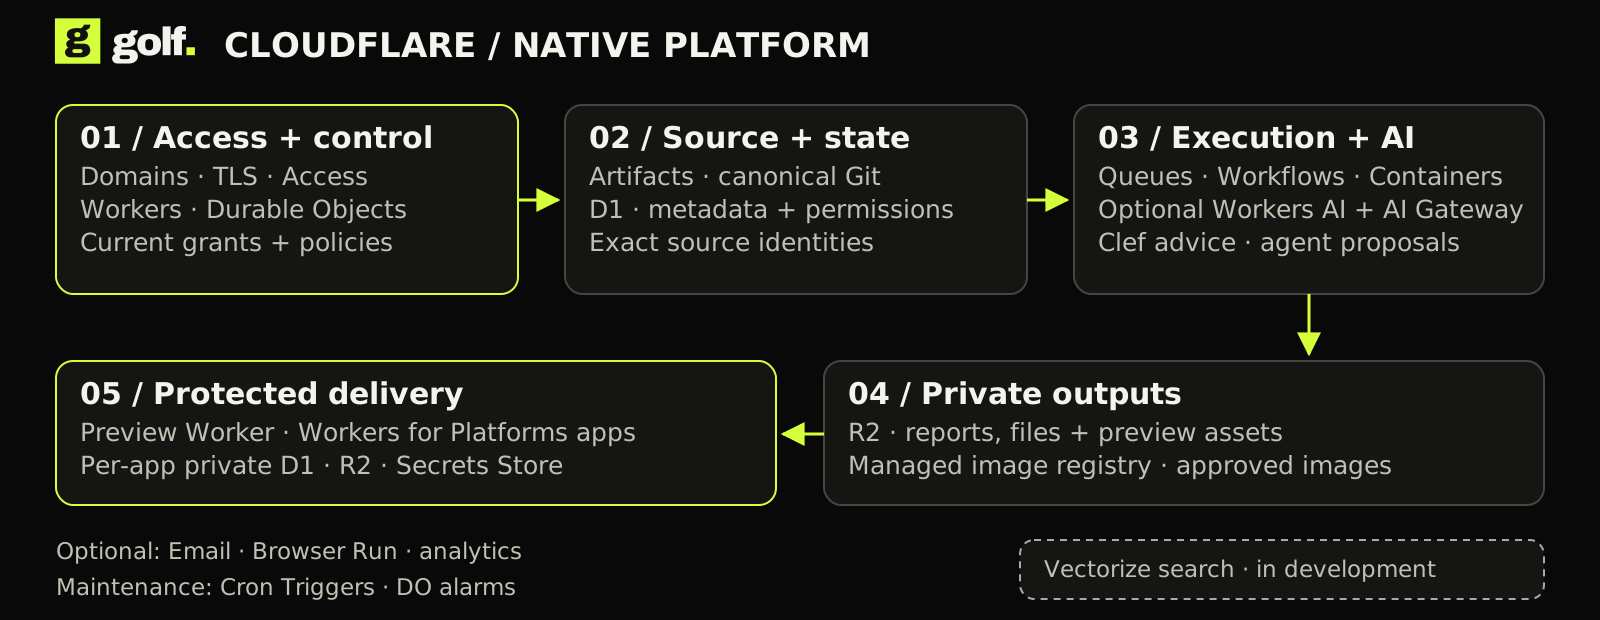
The native platform
How source, authority, execution and protected delivery connect.
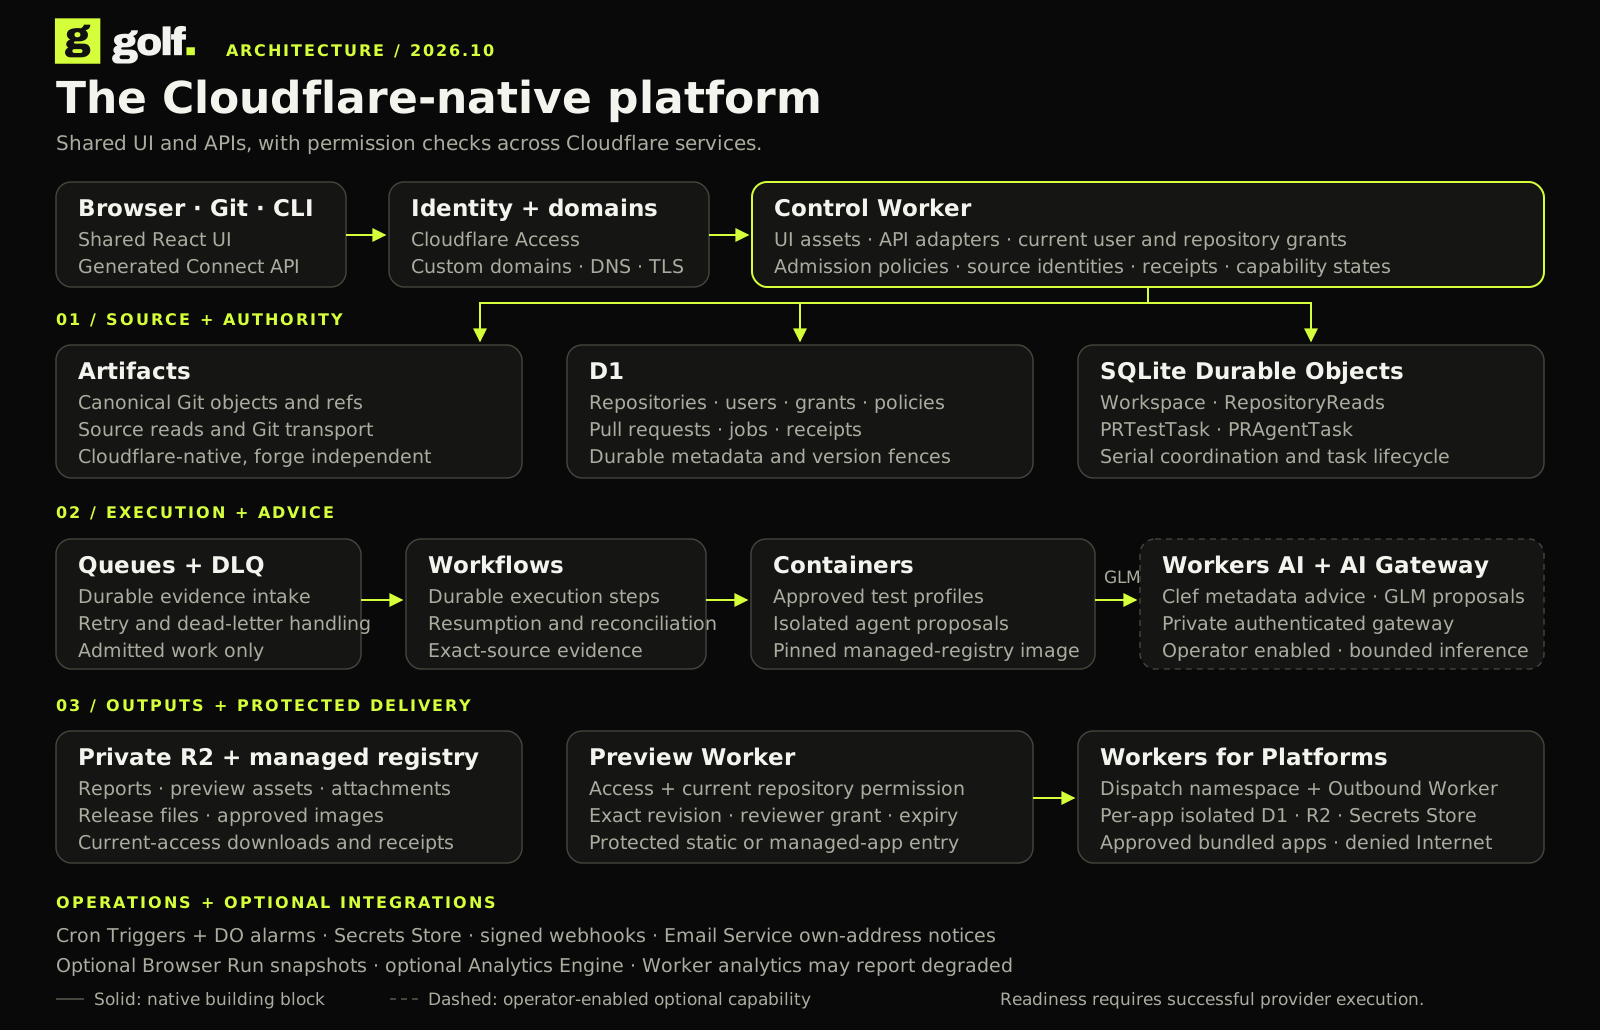
The full Cloudflare architecture
The complete responsibilities and service boundaries.
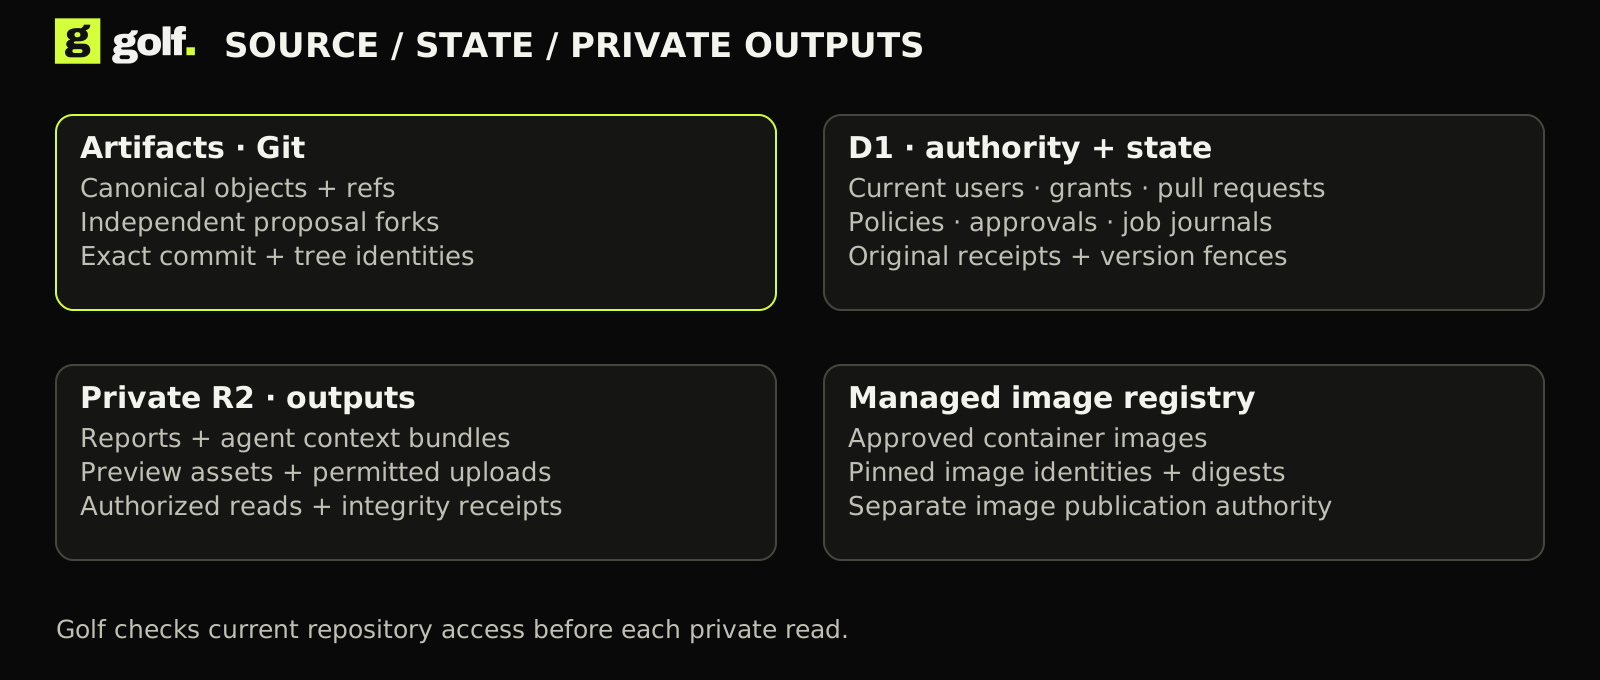
Source, state and private outputs
Artifacts Git, D1 domain state, R2 outputs and managed registry.
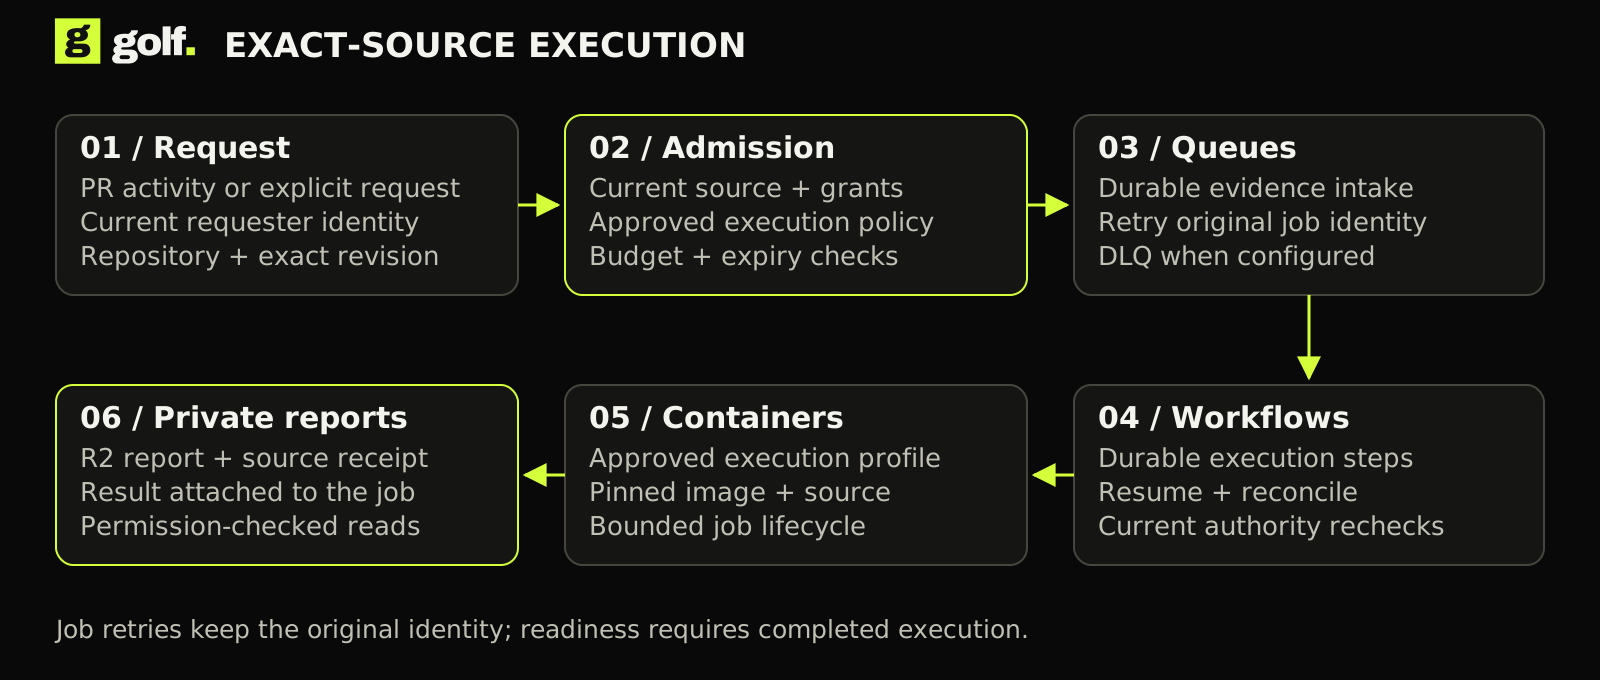
The execution pipeline
Exact-source admission through queue, workflow, container and private evidence.
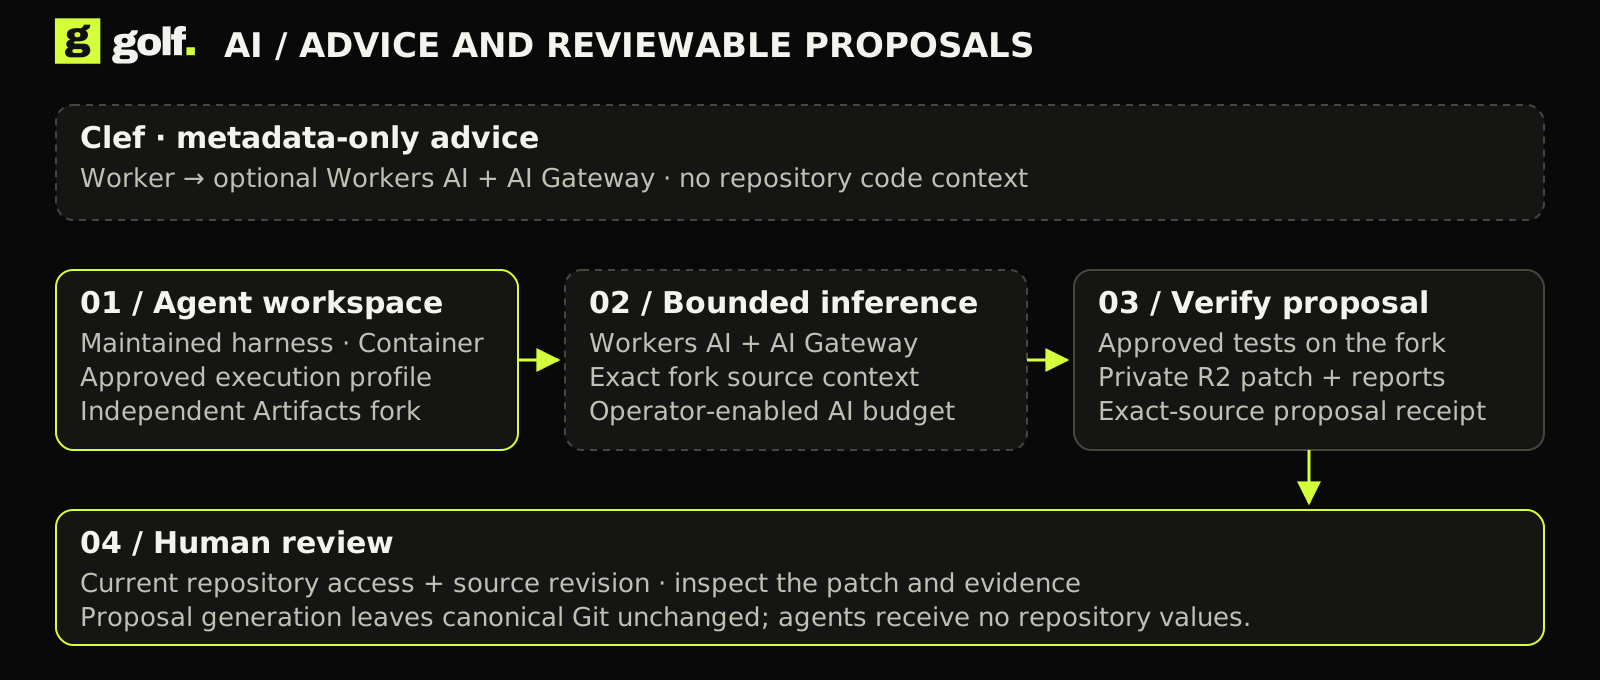
AI advice and proposals
Metadata-only Clef advice and separately tested code proposals.
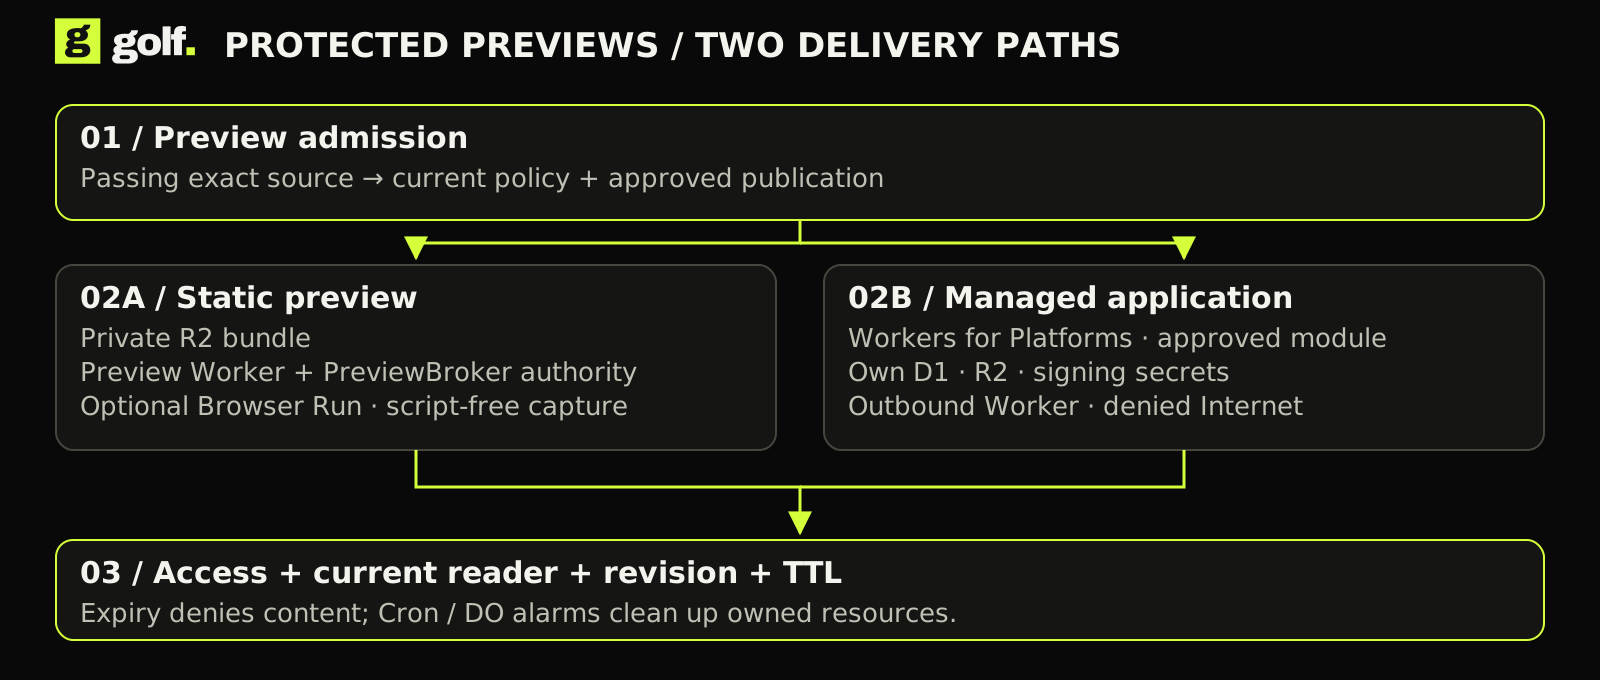
Protected previews
Static and managed application delivery with current reader checks.
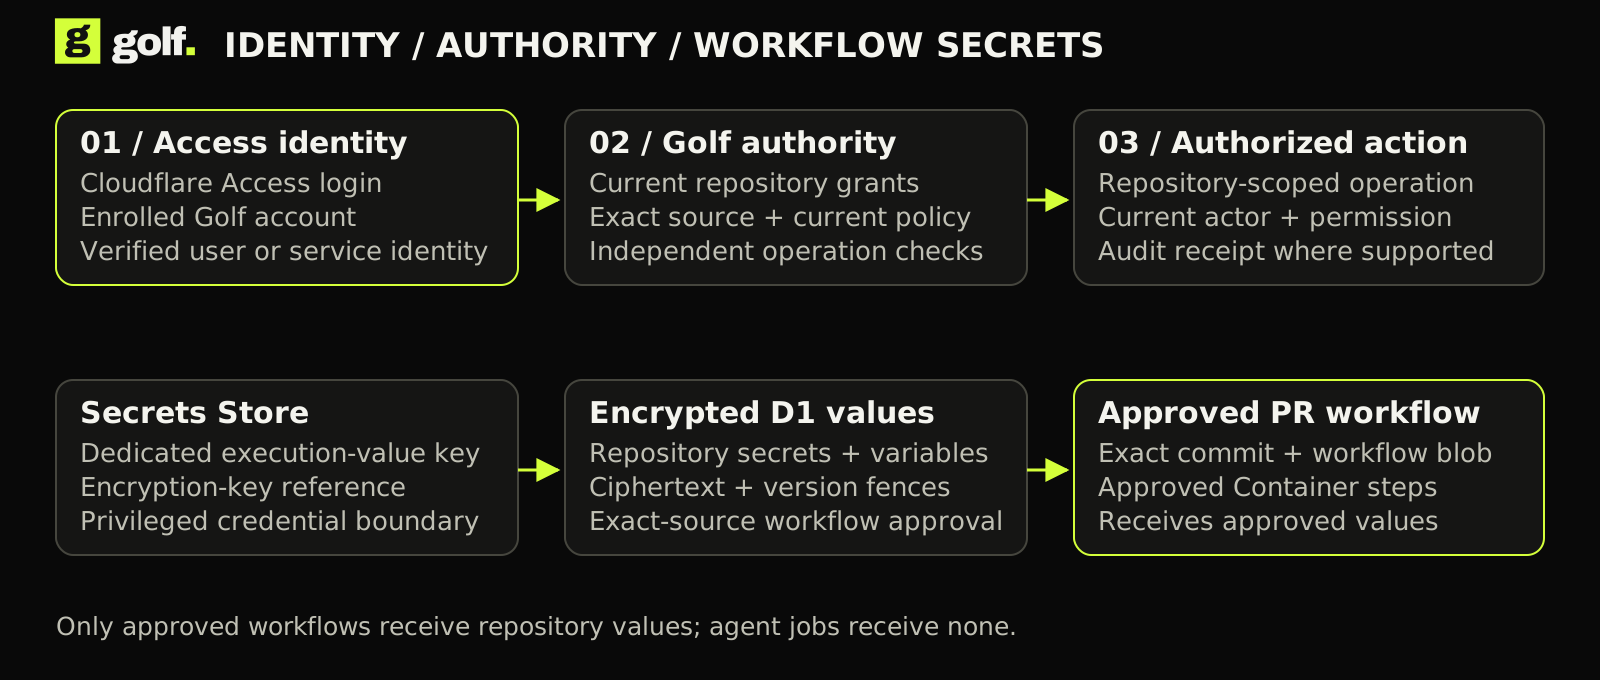
Identity, permission and secret release
Access enrollment, Golf grants and exact-approved workflow values.
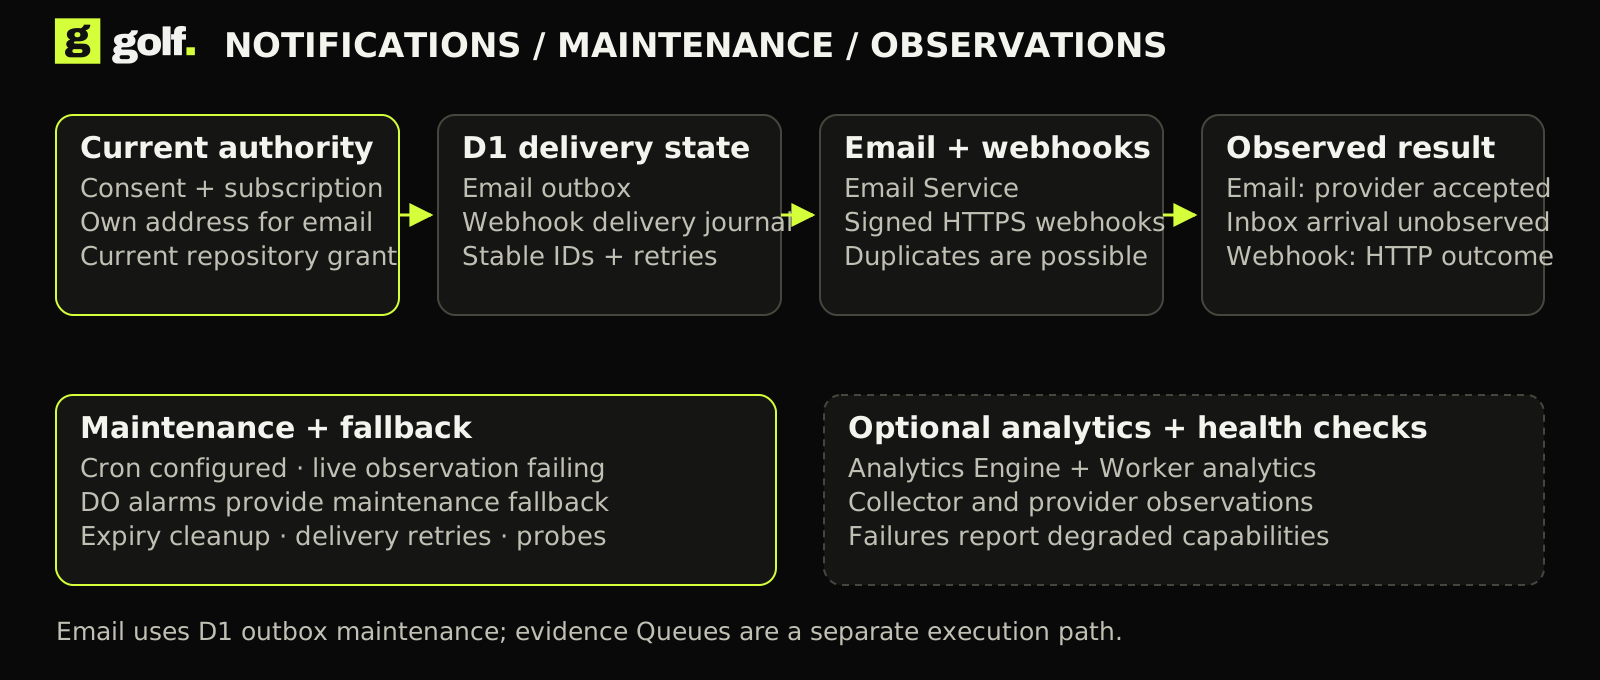
Notifications and maintenance
D1 outboxes, accepted messages and maintenance fallback.
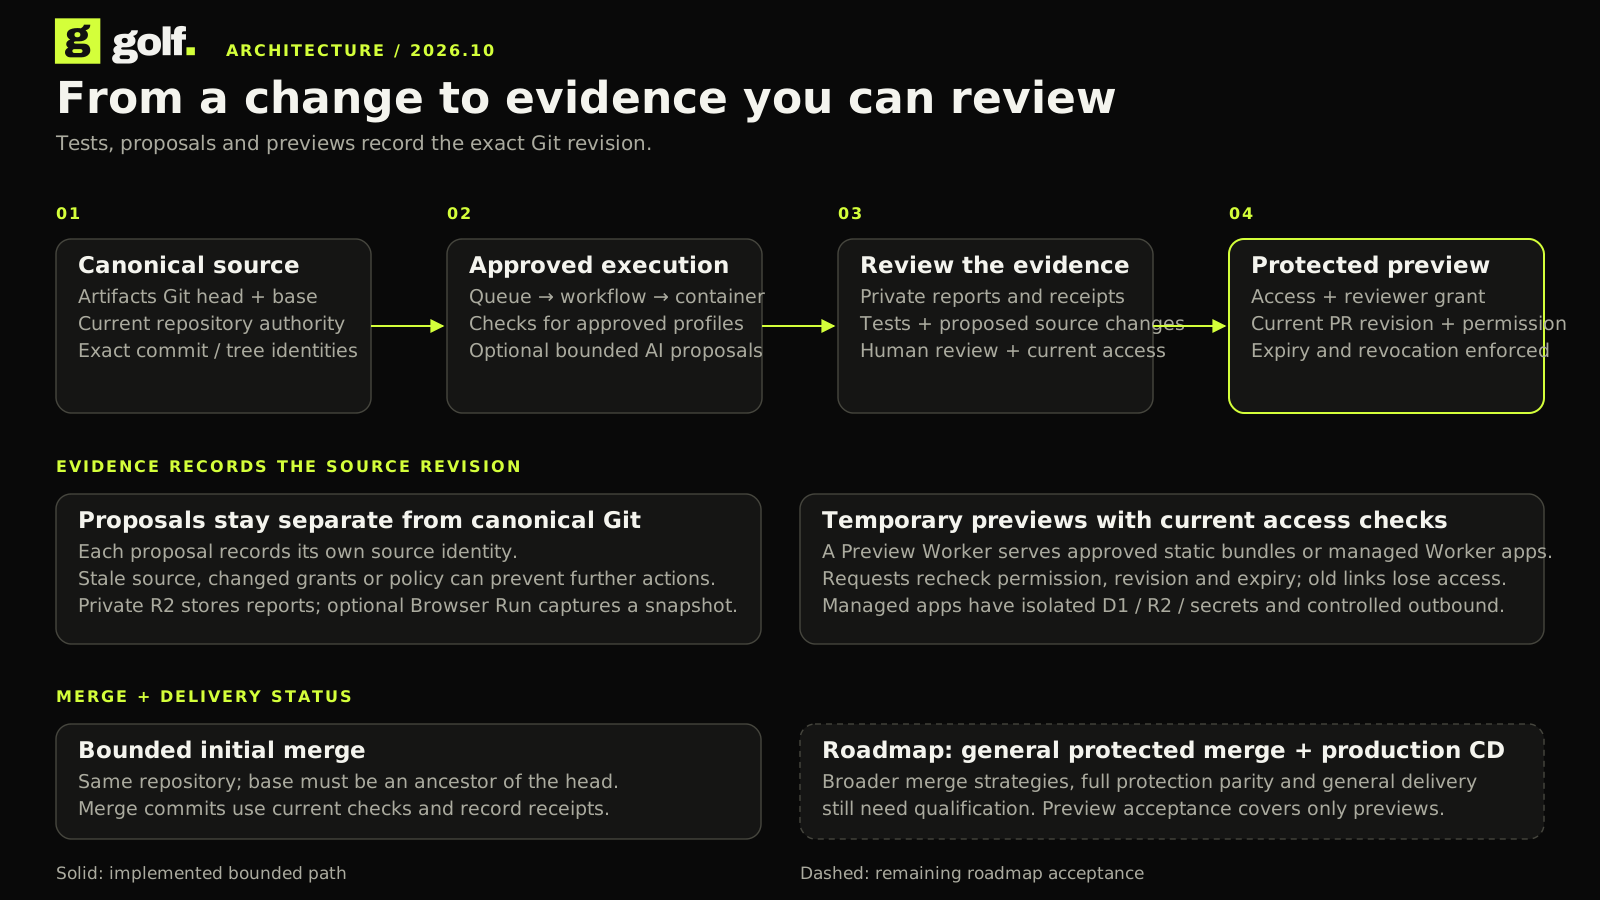
The change lifecycle
Current evidence and previews, with merge/CD acceptance boundaries.
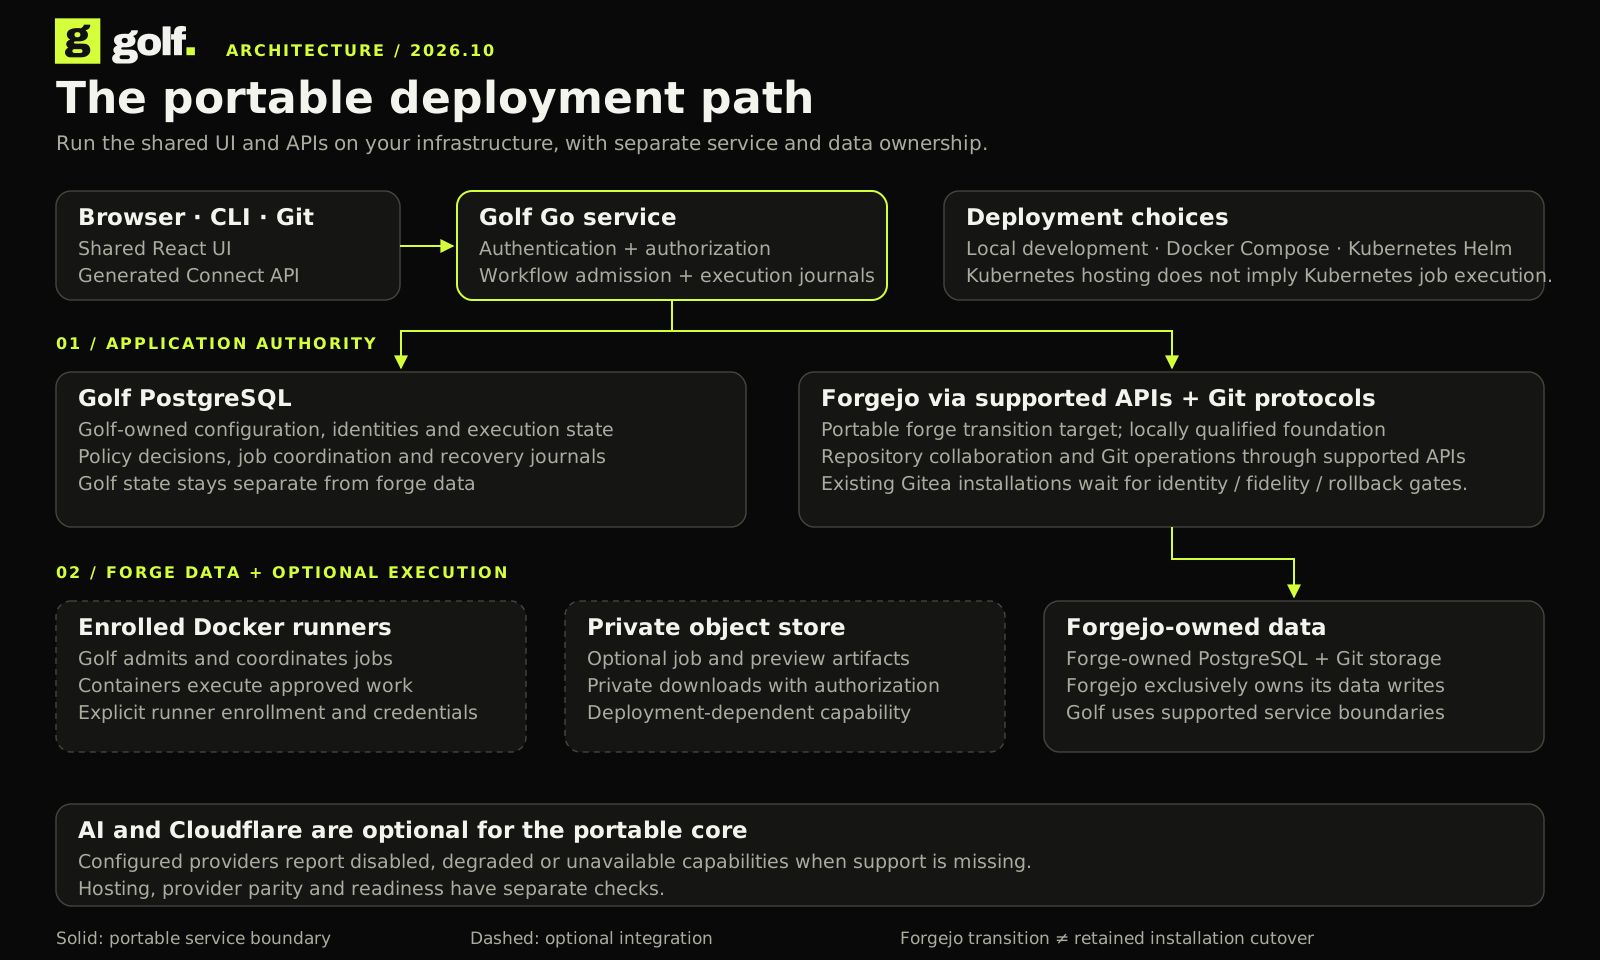
The portable architecture
Forgejo, Go, separate PostgreSQL ownership and optional execution.
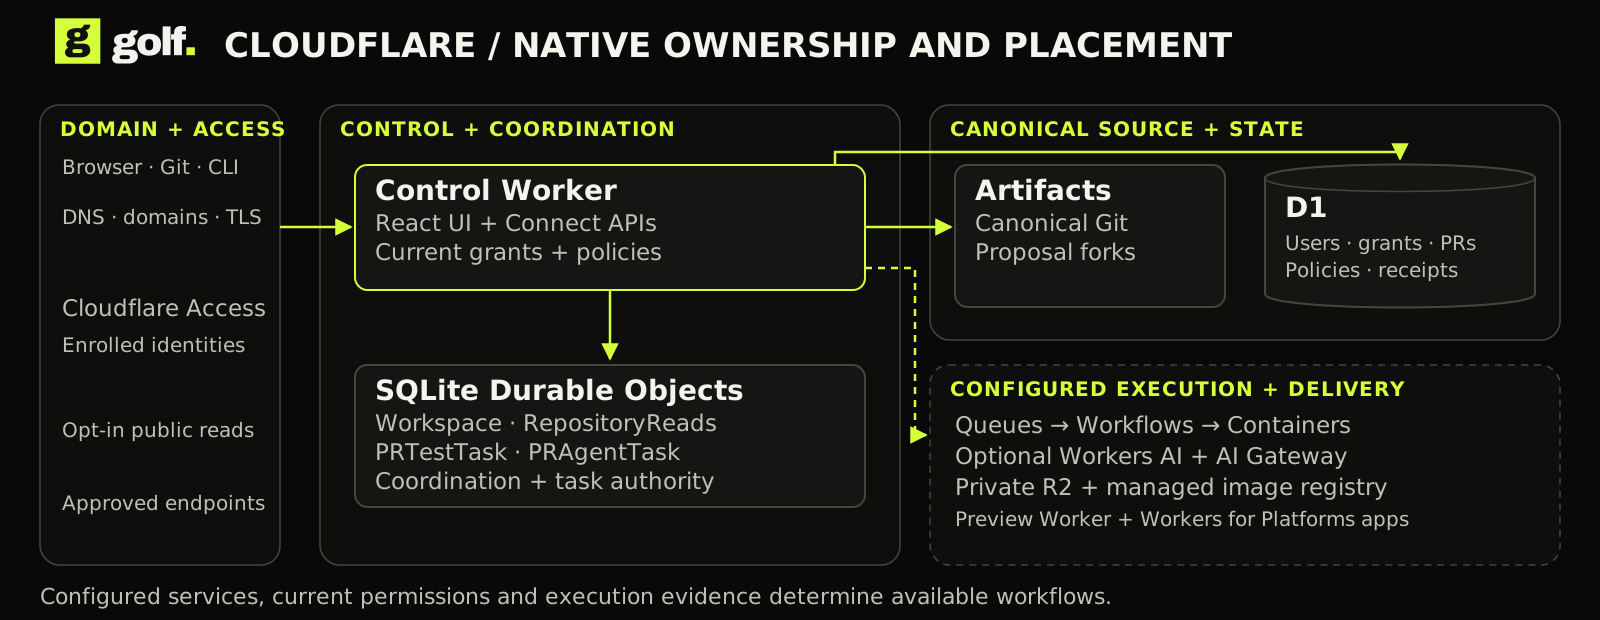
Architectural illustrations
These original illustrations show the architectural ideas in presentation form. Component names, authorization and operational evidence are in the exact diagrams and service reference above.
Four distinct storage responsibilities
Canonical source in Artifacts, domain state in D1, private output in R2 and images in the managed registry each have a separate job.
From an admitted change to private evidence
Queues deliver admitted work, Workflows coordinate its steps, Containers execute the checked source, and R2 retains private outputs.
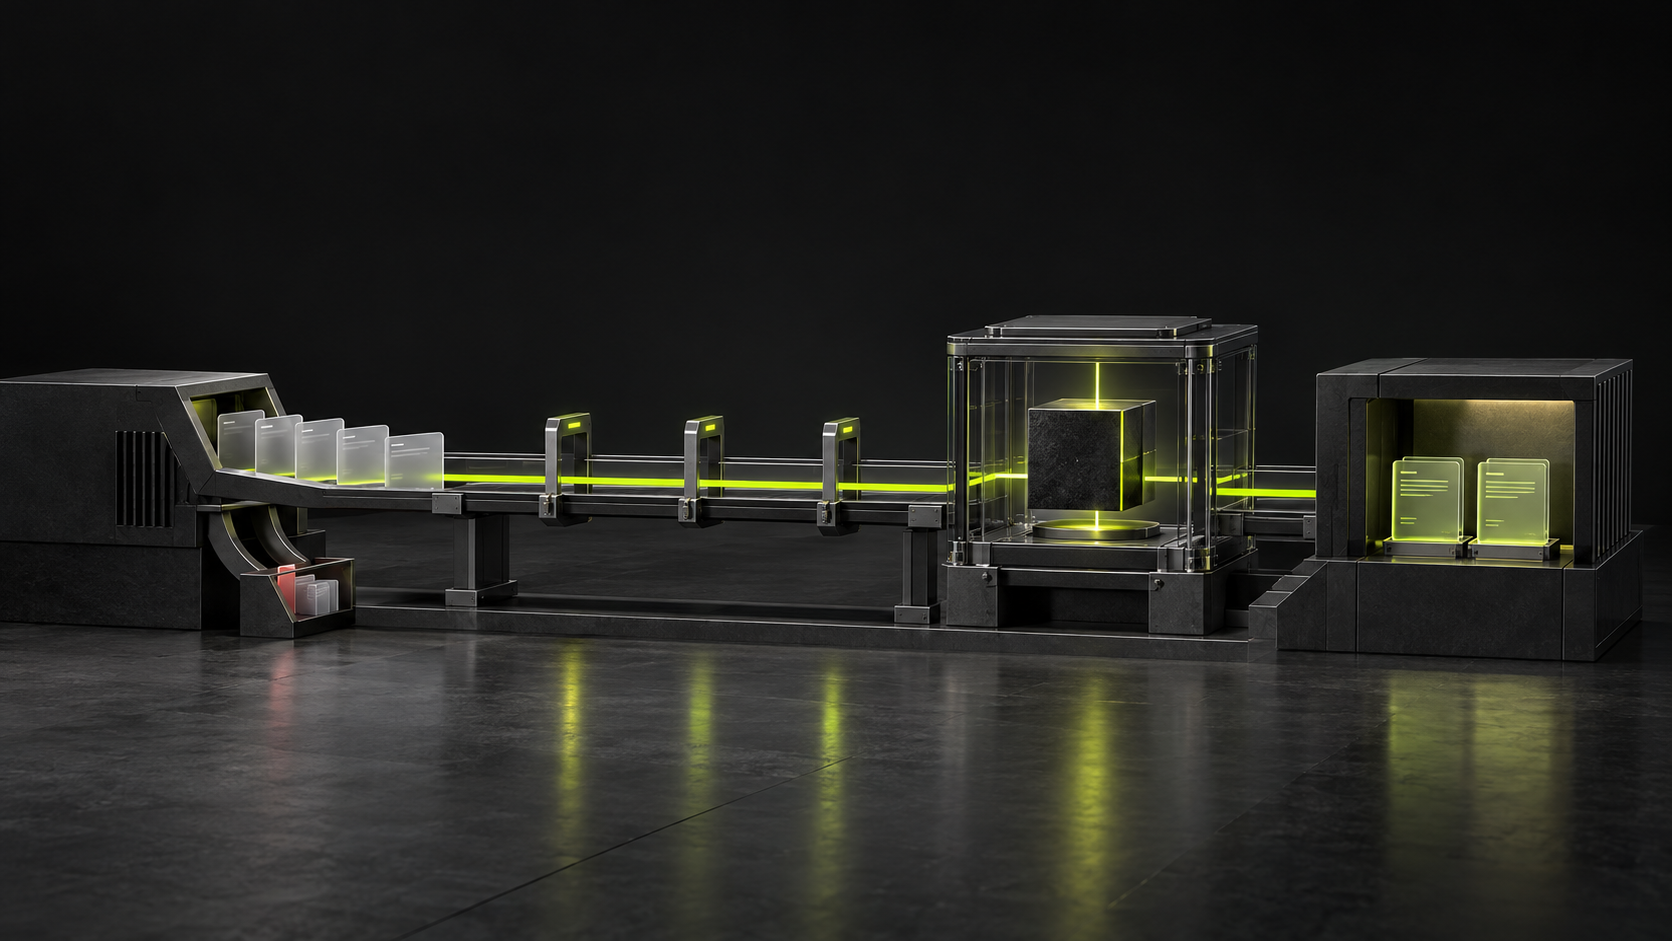
Advice and proposals follow different paths
Clef reads bounded metadata for advice. Code proposals use an independent Artifacts fork, isolated execution and a separate test before human review.
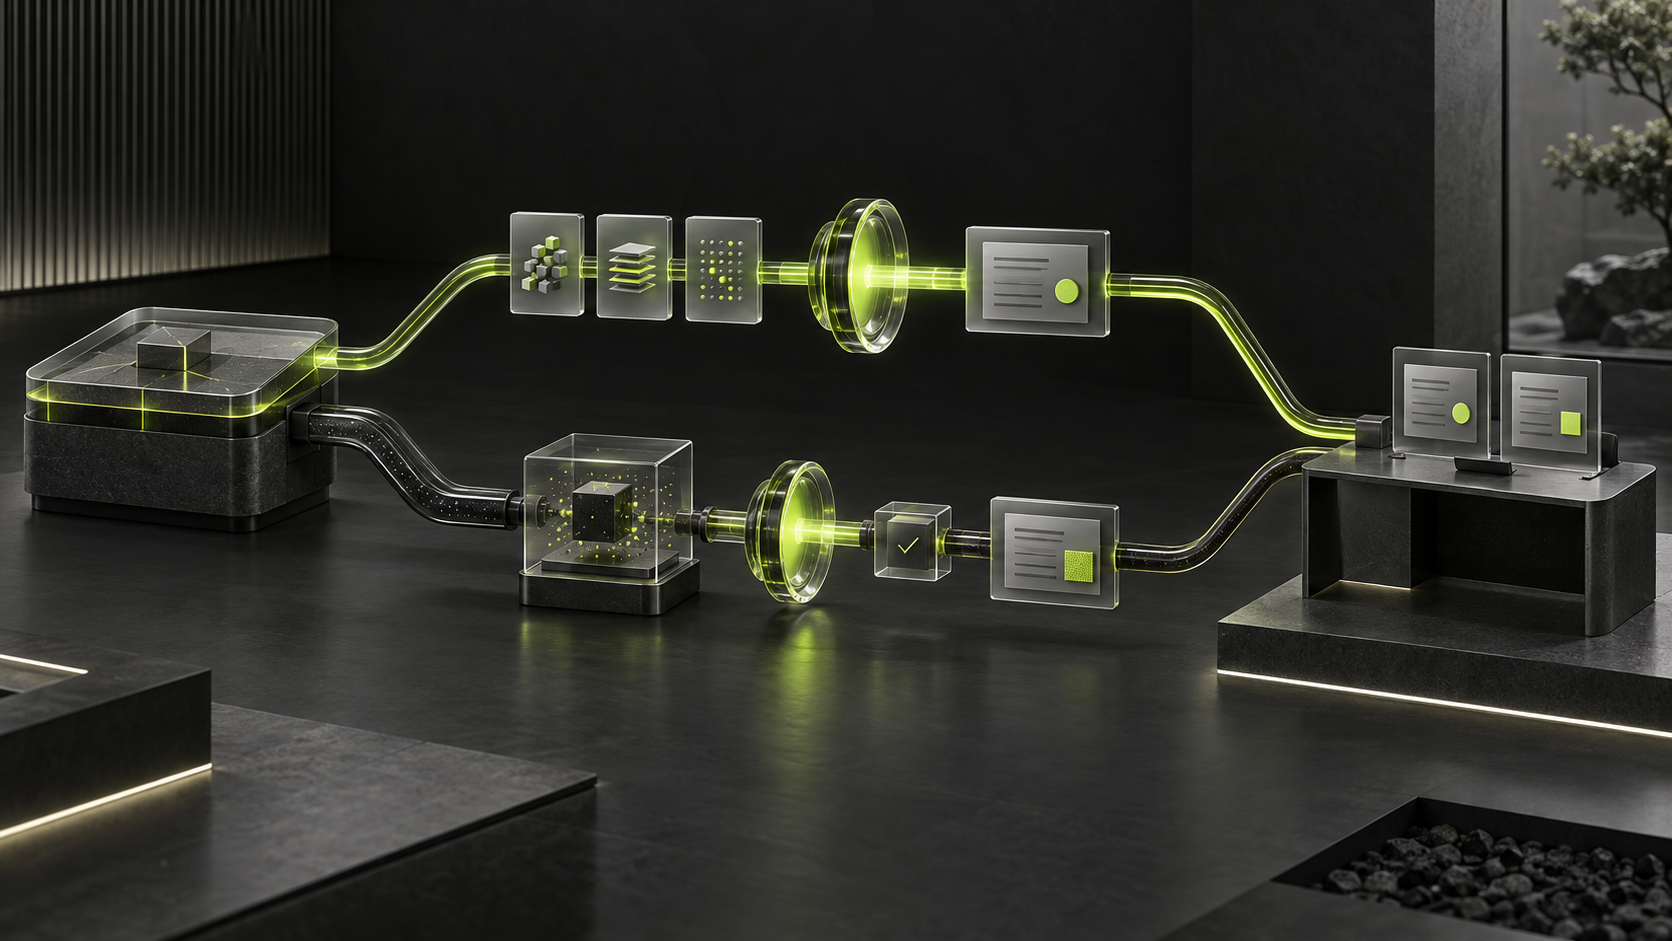
Protected previews have explicit boundaries
Static and Worker previews use distinct serving paths. Worker previews have scoped data, authorization, outbound policy and expiration.
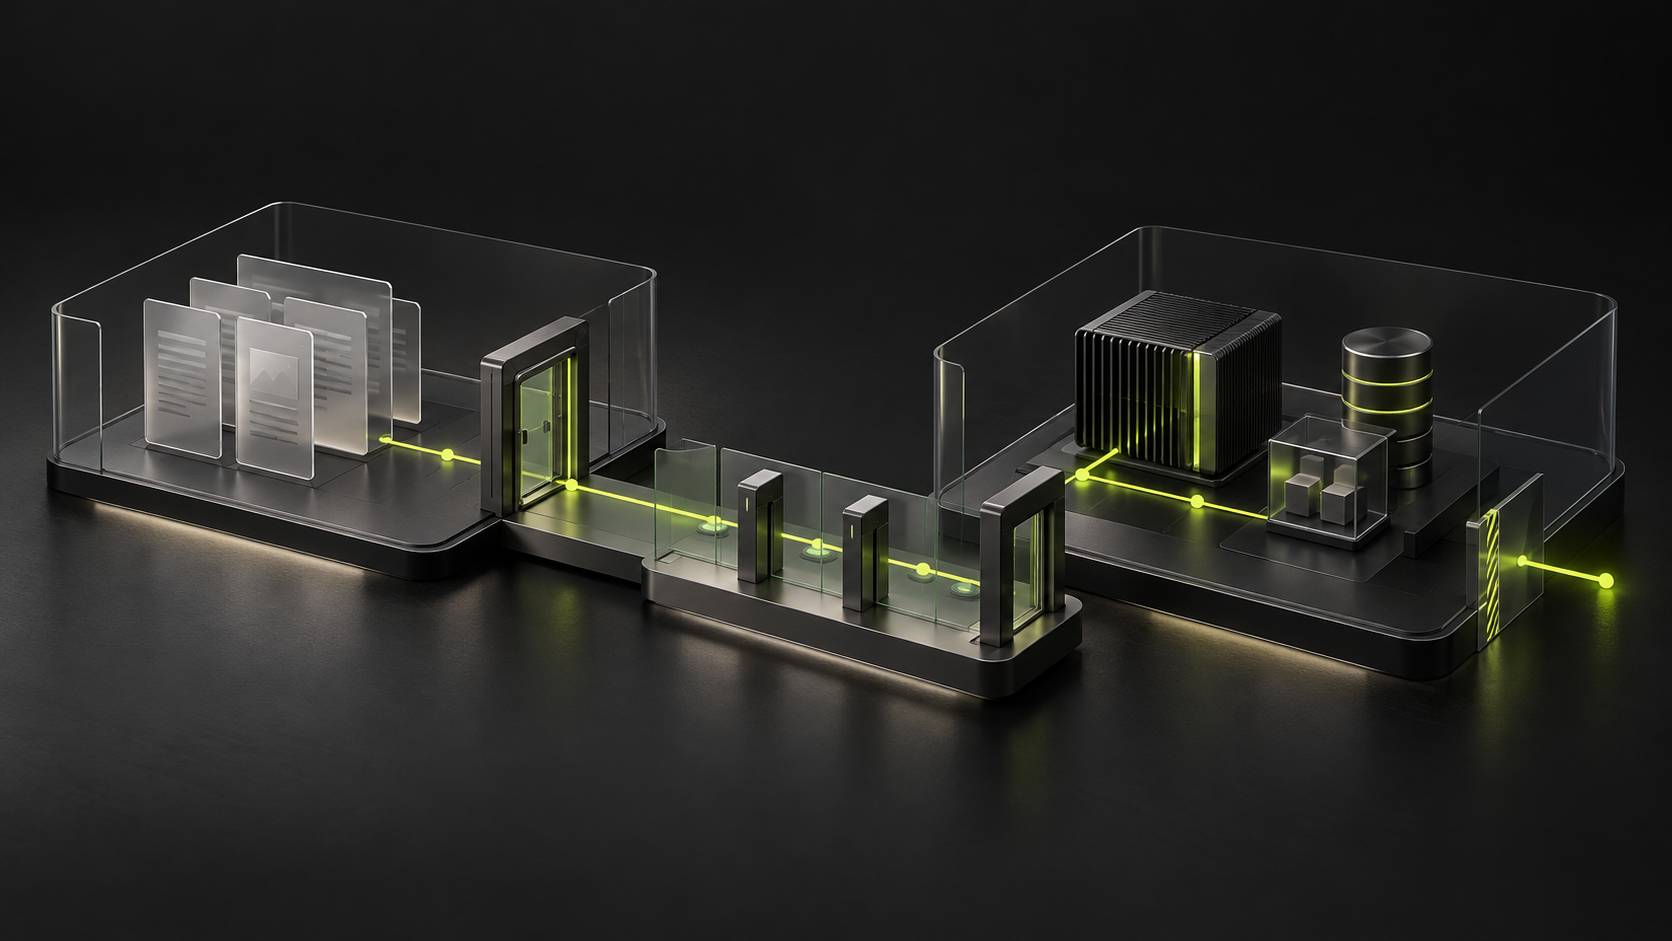
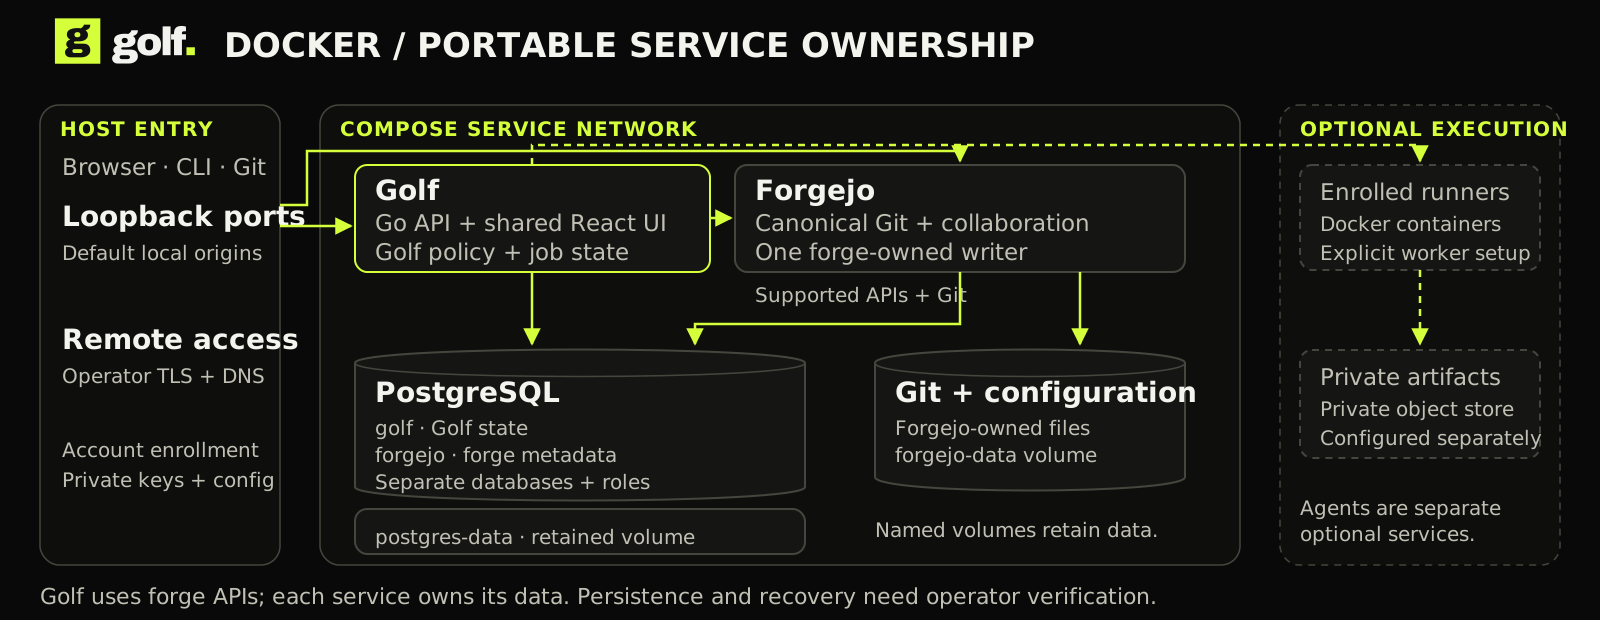
Docker placement and storage
Golf, Forgejo and PostgreSQL run as separate services. Named volumes retain state; execution is separately allocated.
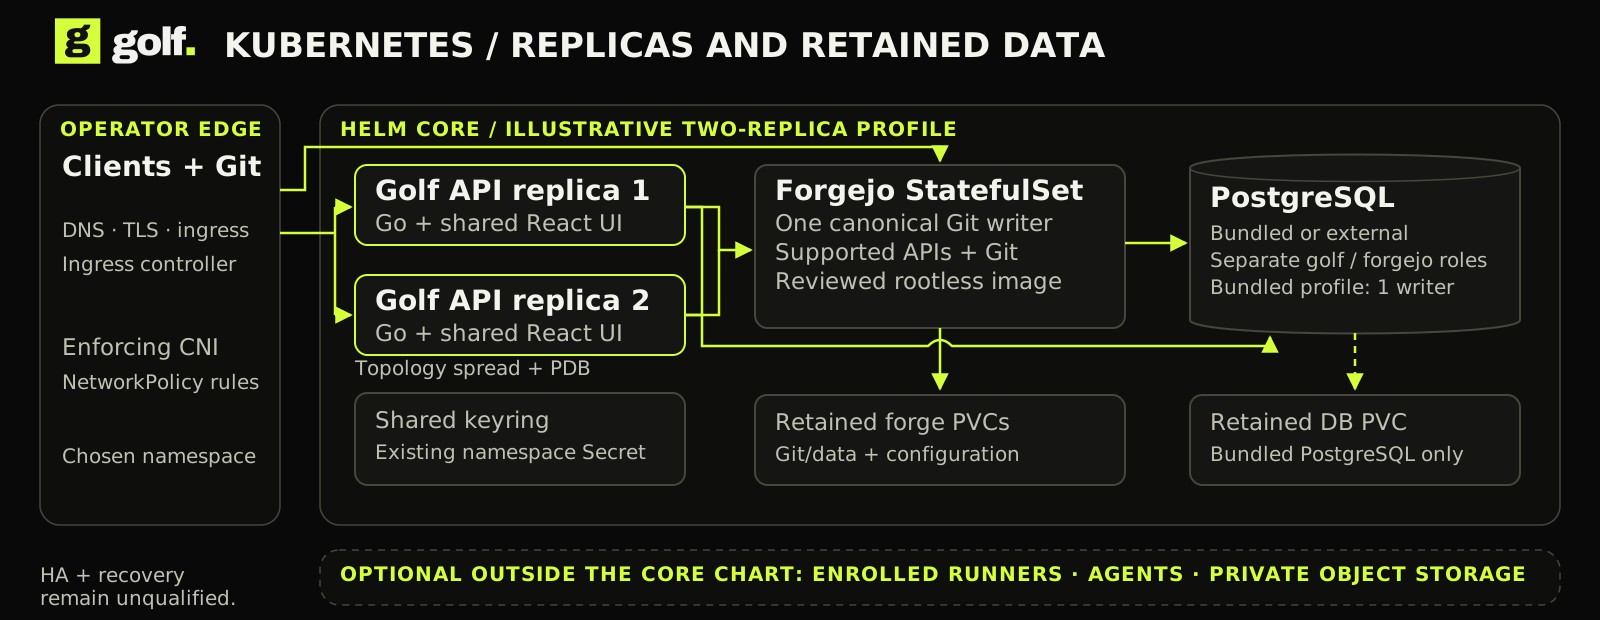
Kubernetes placement and ownership
API replicas share one forge writer and retained PVCs. Spread and disruption controls protect API rollouts; whole-stack HA remains unqualified.
Native Cloudflare placement
Workers own the application, Artifacts owns Git, D1 owns collaboration, and configured provider services execute and deliver work.