Security and ownership
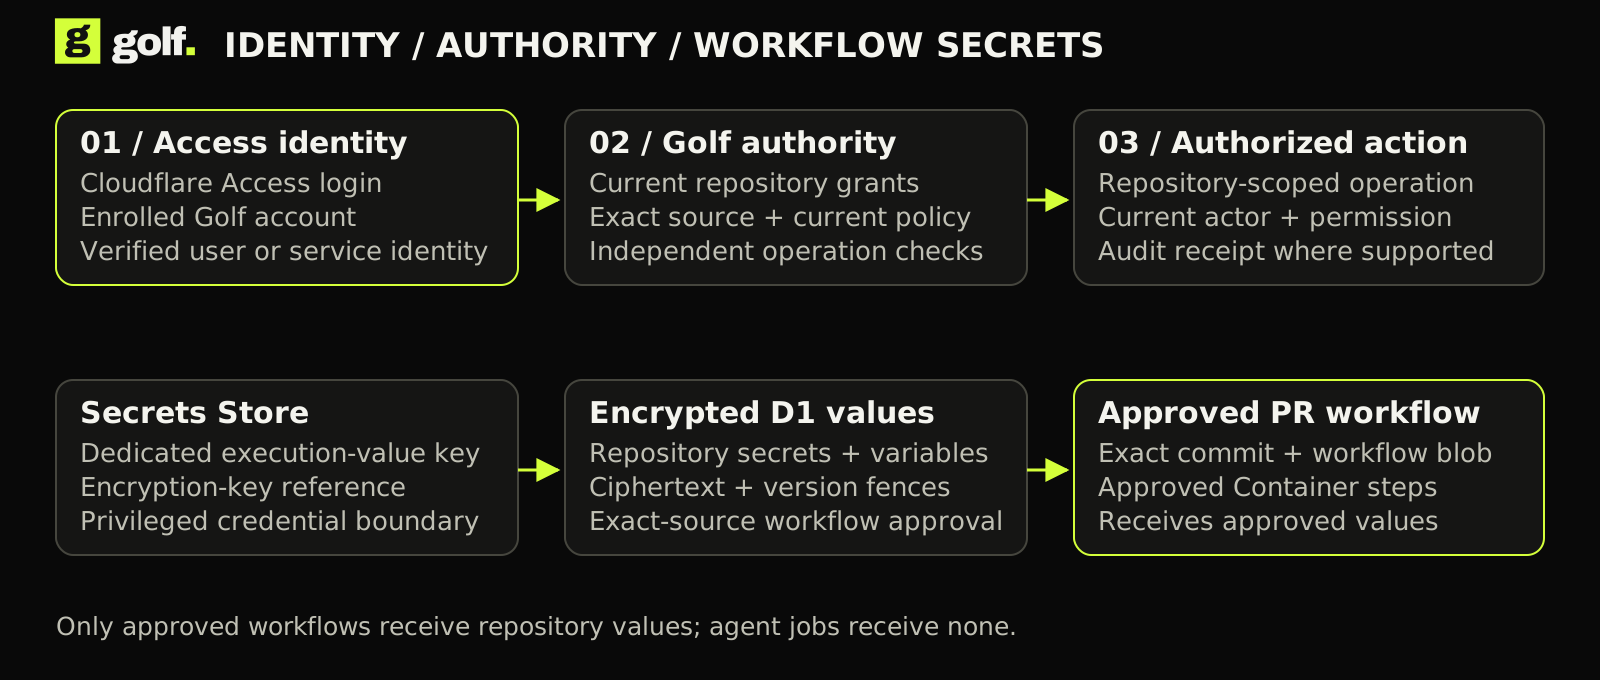
Editable Mermaid source · All architecture diagrams.
Trust boundaries
Native Access authentication and portable Golf sessions identify the caller. Repository ownership, grants, scopes, exact source, sponsorship and policy determine allowed operations. An instance administrator role is not a repository permission override.
Provider credentials stay inside the trusted broker. Native Secrets Store holds authority and encryption keys; portable credentials use the authenticated Golf keyring. Browser state contains neither provider tokens nor native Golf bearer credentials.
Execution and previews
Approved images, isolated workspaces, bounded job leases and explicit networking constrain execution. Independent Artifacts forks hold proposals. Container results and R2 reports retain exact source identity. A passed report does not supply merge or production authority.
Preview entry requires Access plus current Golf reader permission and a live grant. Managed app D1/R2 and signing material are private per preview. Alternate routes cannot bypass protection. Repository preview policy applies at publication/renewal, with incomplete live-policy revocation tracked separately.
Secrets
Exact-commit native workflow approval releases values only to the supported PR profile. Inventories hide secrets; retained logs mask exact text only, not transformations. Rotation, broad environment scopes and arbitrary approved egress remain open. See hosted execution.
Protected-write qualification
The current native same-repository ancestor merge is a bounded standard merge, not full trusted protected publication. Complete review eligibility, immutable candidate checks, protected merge enforcement and broad production CD remain acceptance gates.
Forgejo roles and recovery
Historical provider qualification does not automatically qualify Forgejo roles or recovery. Retained migration uses fresh targets and supported APIs; a private pending review was lost in rehearsal. The documented privileged offline recovery exception requires drained writers and a fresh stopped quarantined target. It permits no forge database or repository-file writes during normal operation.
Public content
Public mode requires explicit repository/profile publication. Private collaboration, tests and previews remain authorized. Rate limiting is approximate per network/location and fails open on limiter errors; it is not a global quota or complete abuse-control system.
See product security/evidence, authentication and recovery.